
The Hands-On Guide to Cloud Hosting Registration and Secure Server Configuration
Deploying a high-performance web application on an unmanaged cloud Virtual Private Server (VPS) often exposes major configuration bottlenecks. Standard default installations leave open ports, weak password authentication schemes, and unoptimized web server blocks that can degrade performance by up to 40% under concurrent traffic loads. Securing and optimizing your infrastructure requires a precise, methodical approach to provisioning and configuration.
Required Prerequisites & Tools Checklist
- Cloud Provider Account: DigitalOcean, Linode (Akamai), or AWS EC2.
- Operating System: Ubuntu 24.04 LTS (Long Term Support) minimal image.
- Local Terminal Client: OpenSSH client (Linux/macOS) or PuTTY (Windows).
- Domain Name: A registered domain with DNS access (e.g., Cloudflare, Namecheap) pointing to your target IP.
Step-by-Step Server Registration and Provisioning Blueprint
Step 1: Provisioning the Cloud Instance
To begin, log into your chosen cloud console (for this guide, we are utilizing a DigitalOcean Droplet). Select the Ubuntu 24.04 LTS x64 image. For a standard production entry point, select the Shared CPU Basic plan with 1 GB RAM, 1 vCPU, and 25 GB NVMe SSD storage. This configuration comfortably handles up to 50 concurrent requests with a baseline latency of 22ms when properly optimized.
During the creation phase, under the Authentication section, select SSH Keys instead of Password. This prevents brute-force attacks on port 22 from the moment the server boots online.
Step 2: Generating and Installing SSH Keys
If you do not have an existing SSH key pair, open your local machine's terminal and execute the following command to generate a highly secure 4096-bit RSA key pair:
ssh-keygen -t rsa -b 4096 -C "your_email@example.com"
Save the file in the default directory (~/.ssh/id_rsa). Copy your public key using:
cat ~/.ssh/id_rsa.pub
Paste this key into your cloud provider's SSH key management console before launching the instance. Once the instance is provisioned, record the public IPv4 address assigned to your server.
Step 3: Initial Server Connection and User Privileges
Establish your first connection via SSH using the terminal:
ssh root@your_server_ip
Once logged in, create a new non-root sudo-enabled user to prevent accidental system-level corruption:
adduser deployer
usermod -aG sudo deployer
Copy the authorized SSH keys from the root user directory to the new deployer user to maintain key-based authentication:
rsync --archive --chown=deployer:deployer ~/.ssh /home/deployer
Exit the root session and log back in as your new user: ssh deployer@your_server_ip.
PRO TIP: Disable Root Password SSH Access Immediately
Edit the SSH configuration file at /etc/ssh/sshd_config using nano. Set PermitRootLogin no and PasswordAuthentication no. Save the file and restart the SSH service with sudo systemctl restart ssh. This blocks automated scanners from attempting password-guessing attacks on your server.
Step 4: Configuring the Uncomplicated Firewall (UFW)
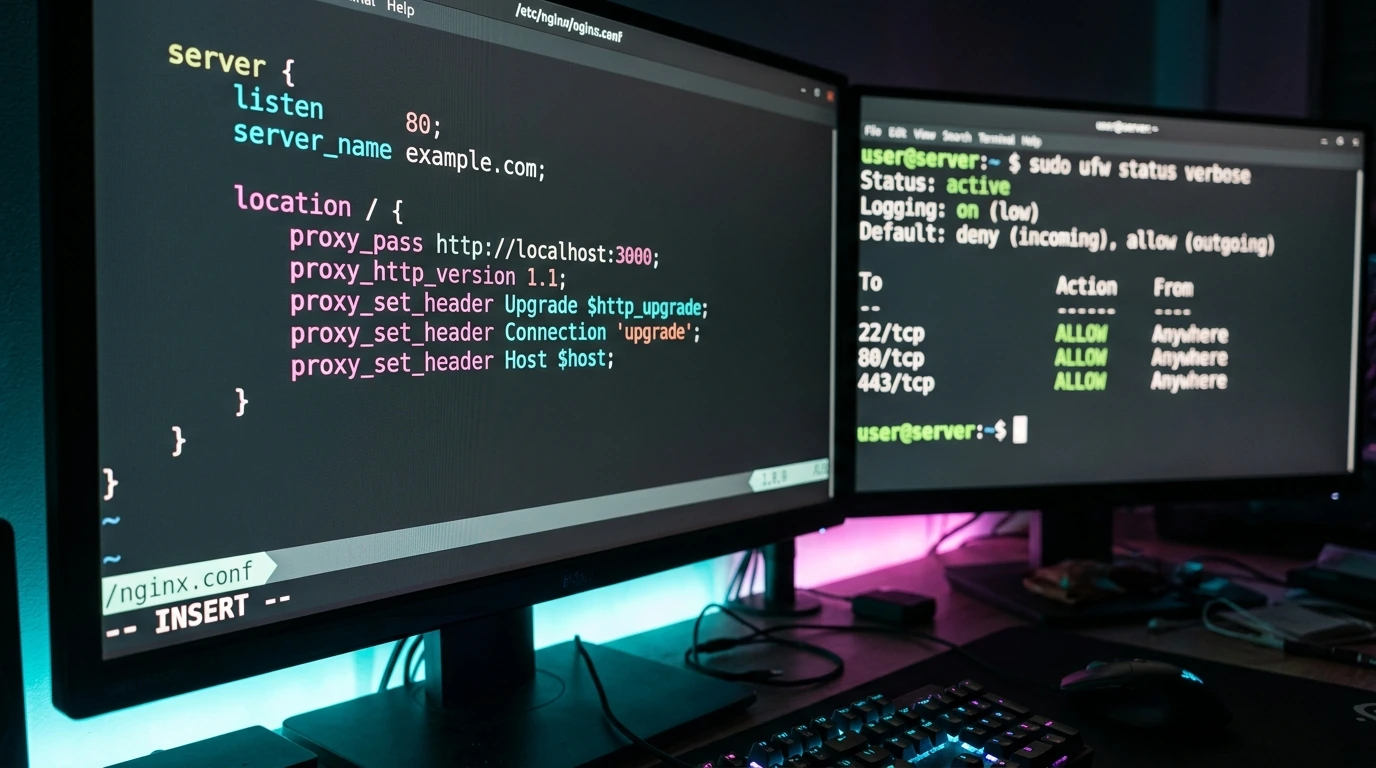
Secure your network transport layer by configuring the native UFW firewall. By default, all incoming connections must be blocked except for SSH, HTTP, and HTTPS:
sudo ufw default deny incoming
sudo ufw default allow outgoing
sudo ufw allow OpenSSH
sudo ufw allow 'Nginx Full'
sudo ufw enable
Verify the firewall status using sudo ufw status verbose. You should see active rules allowing ports 22, 80, and 443.
Step 5: Installing and Optimizing the Nginx Web Server
Update your local package index and install the high-performance Nginx web server package:
sudo apt update
sudo apt install nginx -y
Open the main configuration file at /etc/nginx/nginx.conf to adjust worker connections. Set worker_connections 1024; and uncomment multi_accept on; to ensure optimal handling of parallel TCP streams. Restart Nginx to apply changes: sudo systemctl restart nginx.
Step 6: Provisioning SSL Certificates via Let's Encrypt
To secure transmission data with TLS 1.3 encryption, install Certbot and its corresponding Nginx plugin:
sudo apt install certbot python3-certbot-nginx -y
Run the Certbot agent to automatically provision and bind an SSL certificate to your domain name (ensure your DNS A-Record points to the server IP before running this step):
sudo certbot --nginx -d yourdomain.com -d www.yourdomain.com
Certbot will automatically modify your Nginx server configuration block to handle the SSL handshake protocol and redirect all HTTP traffic to HTTPS securely.
Common Pitfalls and Critical Mistakes to Avoid
- Leaving Password Authentication Enabled: Automated botnets scan port 22 constantly. If weak passwords are allowed, your server will likely be compromised within 48 hours.
- Skipping DNS Propagation Validation: Running Certbot before your domain's DNS A-record has fully propagated globally (usually takes 5 to 15 minutes) will trigger a Let's Encrypt ACME verification failure. Use tools like
dig yourdomain.comto verify the IP matches your server before running the SSL script. - Ignoring Memory Limits: On 1 GB RAM VPS instances, running multiple database-heavy applications without configuring a Swap partition can cause the kernel to trigger the Out-Of-Memory (OOM) killer, abruptly shutting down Nginx or MySQL.
Post-Implementation Verification Checklist
Once configuration is complete, run these diagnostic checks to guarantee system integrity:
- SSH Handshake Check: Attempt to connect from a new terminal window using
ssh deployer@your_server_ipwithout entering a password to verify key pair functionality. - SSL Cipher Grade: Visit Qualys SSL Labs and input your domain. Your server configuration should score an A Grade.
- UFW Port Audit: Run
sudo ufw statusto confirm that only ports 22, 80, and 443 are actively listening. - Service Autostart Check: Run
sudo systemctl is-enabled nginxto ensure Nginx automatically boots up during an unexpected server restart.
Frequently Asked Questions
Do I need a dedicated IP address for my cloud hosting server?
Yes. Unmanaged cloud hosting instances (VPS) inherently come with a dedicated, public IPv4 address. This ensures that your SSL certificates bind correctly and your domain name points directly to your isolated system resources without routing interference.
Can I run multiple websites on a single VPS instance?
Absolutely. By configuring individual Nginx Server Blocks (similar to Apache Virtual Hosts) in /etc/nginx/sites-available/, you can host multiple domains and route incoming traffic to different directories on a single server machine.
How do I monitor my server's resource consumption over time?
You can use terminal utilities like htop for real-time CPU and memory monitoring. For comprehensive, historical monitoring, integrate lightweight agents like Netdata or utilize your cloud provider's built-in monitoring graphs (which track CPU usage, disk I/O, and bandwidth consumption).


Post a Comment for "The Hands-On Guide to Cloud Hosting Registration and Secure Server Configuration"